NETRESEC Network Security Blog - Tag : Netresec

rss Google News

OT Networks Still Need Monitoring

CERT Polska recently published a follow-up report detailing the hack of a Polish combined heat and power (CHP) plant in December 2025.

CERT Polska’s report concludes with several important recommendations, including protecting OT systems through network segmentation and monitoring traffic entering and leaving OT networks. It has now been more than 15 years since I first publicly advocated almost exactly these same two recommendations in my blog post Monitor Those Control System Networks.

One might get the impression that nothing has changed during those 15 years, but I can attest that many OT systems now have effective perimeter protection. Operators of critical infrastructure are also beginning to embrace the concept of network security monitoring for OT systems.

Unfortunately, it appears that the hacked CHP plant in Poland did not have sufficient perimeter protection or network security monitoring in place. The apparent lack of monitoring and logging also left CERT Polska with very limited forensic data. As the report states, “Due to the lack of logs, our investigation relied on the development and testing of hypotheses.” Despite these limitations, I am very impressed by the level of technical detail that CERT Polska were able to reconstruct during their investigation of the CHP hack.

Attack Path

As CERT Polska outline in their report, the attackers’ initial access vector was an Internet-facing FortiGate VPN at a wind farm. From the VPN device, they pivoted via a Teltonika cellular 5G router into a WAGO PLC, which ultimately gave them access to the control system network of a CHP plant.

Attack path from the Internet to the CHP network

Image: Attack path from the Internet to the CHP network

The lack of perimeter protection, which would otherwise have prevented direct connections between different remote sites, gave the attackers access to the PLCs and other industrial equipment that directly controlled the physical process at the CHP plant.

With that type of access, attackers do not need to exploit a vulnerability. They can simply issue “normal” commands over the OT network to shut down the process at the plant. In this specific case, the attackers performed the following operations, apparently in an attempt to cause maximum disruption:

  • Switched multiple Siemens S7 PLCs to STOP mode
  • Enabled password protection on Siemens S7 PLCs to prevent operators from switching them back to RUN mode
  • Changed the configurations of several industrial serial device servers and network switches, making them inaccessible from the network

Siemens S7-1500 PLC in STOP mode, from CERT Polska’s report

Image: Siemens S7-1500 PLC in STOP mode, from CERT Polska’s report

As a result of the attack, a steam turbine and the system used to produce process water in the CHP plant were both shut down on December 29.

Network Security Monitoring

Better perimeter protection might have prevented the initial access path used against the Polish CHP plant. However, it is not always easy for asset owners and operators to identify every boundary around an OT environment or segment it without affecting operations. This is where network security monitoring plays an important role.

OT networks are often well suited to passive monitoring. Most industrial protocols are unencrypted, communication patterns are more deterministic than those in enterprise networks, and traffic volumes are often modest. By monitoring OT network traffic and alerting on suspicious or anomalous behavior and known attack techniques, defenders may be able to detect an intrusion early enough to investigate, contain, and stop it before destructive actions are carried out.

Examples of useful detections include:

  • Reconnaissance activity, such as TCP SYN scans
  • Attempts to access canary or honeypot systems that normal operations should not touch
  • Connections from unexpected systems to ICS-specific ports, such as TCP ports 102, 502, 2404, 5094, 20000, 44818 and 47808
  • Potentially dangerous protocol commands, such as putting a PLC into STOP mode, changing its operating mode, downloading a new program, or modifying its configuration outside a scheduled maintenance window
  • New communication paths, such as traffic between IP address pairs that have not previously communicated

The Polish incident illustrates the value of detecting reconnaissance activity, not just the final destructive commands. The disruptive actions occurred on December 29, but CERT Polska uncovered malicious activity as early as December 18.

Log from the Teltonika RUTX50 cellular router

Image: Log from the Teltonika RUTX50 cellular router

This suggests that the attackers had access to the environment more than 10 days before the destructive actions. This period is known as the dwell time: the time between an attacker gaining access to an environment and being detected or taking disruptive action.

Had the intrusion been detected early, this dwell time would have provided multiple opportunities for defenders to contain it before the attackers carried out their disruptive actions.

Long dwell times are common in attacks against OT systems. Attackers may spend weeks or months learning about the environment, identifying important assets, and determining how to disrupt the physical process. In some cases, access to critical infrastructure is established as part of pre-positioning, where a state-sponsored threat actor gains and maintains access to an OT environment without immediately causing disruption, preserving the ability to deliver a destructive payload at a later point. This makes early detection especially important, even when an intrusion does not initially appear to be affecting plant operations.

Captured network traffic, preferably stored as PCAP files, is one of the most valuable sources of evidence when analyzing a suspected attack against an OT system. It can help investigators reconstruct the attacker’s activity, validate alerts, and identify affected systems. If the captured traffic is stored on a system that is not accessible from the OT network, the risk of an attacker tampering with the evidence is reduced.

This is one reason we have been teaching Network Forensics for Industrial Control Systems for more than 10 years. Feel free to reach out if you want to learn more about our network forensics training.

Siemens S7 Advisory

On a related note, the NSA, CISA, FBI, DOE, and EPA published a joint cybersecurity advisory titled Defending Against an Active Threat to Siemens S7 Series PLCs on August 19 (PDF). In the advisory, the authoring agencies called for mitigation measures such as verifying network segmentation and monitoring network traffic to detect and alert on anomalous or malicious activity. These recommendations are very much in line with what CERT Polska stated in their report, as well as with what I have been recommending since 2011.

The question isn't whether we should implement these recommendations, 15+ years of evidence answers that. The question is what it will take to make them happen.

Posted by Erik Hjelmvik on Monday, 31 August 2026 11:50:00 (UTC/GMT)
Tags: #Netresec #NSM #ICS #ASCII-art

Short URL: https://netresec.com/?b=2686c28


Decoding malware C2 with CyberChef

This video tutorial demonstrates how malware XOR encrypted and obfuscated C2 traffic can be decoded with CyberChef.

The analyzed PCAP files can be downloaded from malware-traffic-analysis.net.

CyberChef recipe to decode the reverse shell traffic to 103.27.157.146:4444:

From_Hex('Auto')
XOR({'option':'Hex','string':'62'},'Standard',false)
Find_/_Replace({'option':'Regex','string':'\\r'},'',true,false,true,false)
From_HTML_Entity()

Decoded data from first "key007" reverse shell session to 103.27.157.146:4444:

key007
Authentication successful
furtheringthemagic.com
net group "domain computers" /domain
The request will be processed at a domain controller for domain furtheringthemagic.com.

Group name Domain Computers
Comment All workstations and servers joined to the domain

Members

-------​--------​-------​--------​-------​---------​-------​----------​--------​--------
DESKTOP-G71S4PF$
The command completed successfully.

CyberChef recipe to decode obfuscated PowerShell payload from malicious finger service on 64.190.113.206:79:

Fork(',','',false)
Pad_lines('End',5,',6044')
Subtract('Comma')
From_Charcode('Space',10)

Update 2026-01-21

Our classification of the final payload has been updated from AsyncRAT to GhostWeaver thanks to feedback from Don Pasci. Don referenced a writeup by Recorded Future's Insikt Group, called Uncovering MintsLoader With Recorded Future Malware Intelligence Hunting, which states the following:

GhostWeaver has periodically been misclassified as AsyncRAT. [...] GhostWeaver and AsyncRAT share certain characteristics within their self-signed X.509 certificates, such as identical expiration dates and serial number lengths; however, these similarities may simply reflect common certificate-generation methods rather than meaningful operational overlap.

We also believe that some of the PowerShell related traffic was caused by MintsLoader.

Update 2026-08-11

The analyzed XOR C2 protocol now has a name. It's called "XorBee RAT". See this writeup by Randy McEoin for more details.

IOC List

  • 103.27.157.146:4444 (XorBee RAT reverse shell)
  • 64.190.113.206:79 (finger)
  • checkifhuman[.]top (finger)
  • ey267te[.]top (MintsLoader)
  • 64.52.80.153:80 (MintsLoader)
  • 173.232.146.62:25658 (AsyncRAT GhostWeaver)
  • 08kcbghk807qtl9[.]fun:25658 (AsyncRAT GhostWeaver)

Network Forensics Training

Check out our network forensic trainings if you want to learn more about decoding malware C2 traffic. I'm teaching a live online Network Forensics for Incident Response class on February 23-26.

Posted by Erik Hjelmvik on Tuesday, 20 January 2026 12:10:00 (UTC/GMT)

Tags: #Netresec #CyberChef #XOR #PCAP #CapLoader #PowerShell #Video #videotutorial

Short URL: https://netresec.com/?b=261f535


Network Forensics Training - Spring 2024

PCAP in the Morning - March 4-7 and 25-28

I will teach two live online network forensics classes in March, one on European morning time, and the other on US morning time. The subject for both classes is network forensics in an incident response context.

The training is split into four interactive morning sessions, so that you have the afternoon free to either practice what you learned in class or catch up with your “normal” day job. The number of attendees will be limited in order to provide a good environment for taking questions. A maximum of 15 attendees will be accepted per class. The registration will be closed once we reach this attendee limit.

  • 🇪🇺 March 4-7, 2024: PCAP in the Morning Europe
    ⏲️ Time: 8:30 AM to 12:30 PM CET
    💸 Price: € 930 EUR per student
  • 🇺🇸 March 25-28, 2023: PCAP in the Morning US
    ⏲️ Time: 9:30 AM to 1:30 PM EDT
    💸 Price: $1,000 USD per student

We will be analyzing a unique 30GB PCAP data set captured during June 2020 on an Internet connected network with multiple clients, an AD server, a web server, an android tablet and some embedded devices. As you’ve probably guessed, the capture files contain traffic from multiple intrusions by various attackers, including APT style attackers and botnet operators. The initial attack vectors are using techniques like exploitation of web vulnerabilities, spear phishing, a supply chain attack and a man-on-the-side attack! In this training you'll get first-hand experience looking at C2 and backdoor protocols, such as Cobalt Strike, TrickBot, njRAT and Meterpreter.

See our training page for more info about the “PCAP in the Morning” classes.

To sign up for a class, simply send an email to sales@netresec.com with the class dates, your name and invoice address. We will then send you a PayPal payment link that you can use to complete your training registration.

Hope to see you there!

Erik H

Cheers,
Erik Hjelmvik
Creator of NetworkMiner and founder of Netresec

Posted by Erik Hjelmvik on Monday, 11 December 2023 12:55:00 (UTC/GMT)

Tags: #Netresec #PCAP #Training #Network Forensics #Class

Short URL: https://netresec.com/?b=23C9979


Online Network Forensics Class

I will be teaching two live online network forensics classes this spring, one in March and one in April. The March class is adapted to American time and the April one is adapted to European time. Both classes focus on doing network forensics in an incident response context.

Network Forensics for Incident Response

The training is split into four interactive morning sessions, so that you have the afternoon free to either practice what you learned in class or do your “normal” day job. The number of attendees will be limited in order to enable attendees to ask questions or even cover short ad-hoc side tracks. We plan to accept 10 to 15 attendees per class. The class registration will be closed once we reach this attendee limit.

  • 🇺🇸 March 20-23, 2023: PCAP in the Morning US
    ⏲️ Time: 9:30 AM to 1:30 PM EDT
    💸 Price: $1,000 USD per student
  • 🇪🇺 April 17-20, 2023: PCAP in the Morning Europe
    ⏲️ Time: 8:30 AM to 12:30 PM CEST
    💸 Price: € 950 EUR per student

We will be analyzing a unique 30GB PCAP data set captured during June 2020 on an Internet connected network with multiple clients, an AD server, a web server, an android tablet and some embedded devices. As you’ve probably guessed, the capture files contain traffic from multiple intrusions by various attackers, including APT style attackers and botnet operators. The initial attack vectors are using techniques like exploitation of web vulnerabilities, spear phishing, a supply chain attack and a man-on-the-side attack!

See our training page for more info about the “PCAP in the Morning” classes.

To sign up for a class, simply send an email to sales@netresec.com with the class dates, your name and invoice address. We will then send you a PayPal payment link that you can use to complete your training registration.

Hope to see you there!

Erik H

Cheers,
Erik Hjelmvik
Creator of NetworkMiner and founder of Netresec

Posted by Erik Hjelmvik on Tuesday, 17 January 2023 10:18:00 (UTC/GMT)

Tags: #Netresec #PCAP #Training #Network Forensics #Class

Short URL: https://netresec.com/?b=2312e4f


Network Forensics Classes for EU and US

We have now scheduled two new live online classes, one in September and one in October. The September class is adapted to European time and the October one is adapted to American time. The contents are exactly the same in both classes.

PCAP in the mornining

The training is split into four interactive morning sessions (4 hours each), so that you have the afternoon free to either practice what you learned in class or do your “normal” day job. The number of attendees will be limited in order to enable attendees to ask questions or even cover short ad-hoc side tracks. We plan to accept something like 10 to 15 attendees per class. The class registration will be closed once we reach this attendee limit.

  • 🇪🇺 September 20-23, 2021. Live Online Training "PCAP in the Morning EU"
    ⏲️ Time: 8:30 AM to 12:30 PM CET (Central European Time)
    💸 Price: € 820 EUR per student (€ 738 EUR if registering before August 20)
  • 🇺🇸 October 25-28, 2021. Live Online Training "PCAP in the Morning US"
    ⏲️ Time: 9:00 AM to 1:00 PM EDT (US Eastern Daylight Time)
    💸 Price: $1,000 USD per student ($900 USD if registering before September 25)

We will be analyzing a unique 30GB PCAP data set captured during June 2020 on an Internet connected network with multiple clients, an AD server, a web server, an android tablet and some embedded devices. As you’ve probably guessed, the capture files contain traffic from multiple intrusions by various attackers, including APT style attackers and botnet operators. The initial attack vectors are using techniques like exploitation of web vulnerabilities, spear phishing, a supply chain attack and a man-on-the-side attack!

See our training page for more info about the “PCAP in the Morning” classes.

To sign up for a class, simply send an email to sales@netresec.com with the class dates, your name and invoice address. We will then send you a PayPal payment link that you can use to complete your training registration.

Hope to see you there!

Erik H

Cheers,
Erik Hjelmvik
Creator of NetworkMiner and founder of Netresec

Posted by Erik Hjelmvik on Monday, 07 June 2021 09:55:00 (UTC/GMT)

Tags: #Netresec #PCAP #Training #Network Forensics #Class

Short URL: https://netresec.com/?b=216851d


Detecting Cobalt Strike and Hancitor traffic in PCAP

This video shows how Cobalt Strike and Hancitor C2 traffic can be detected using CapLoader.

I bet you’re going:

😱 OMG he’s analyzing Windows malware on a Windows PC!!!

Relax, I know what I’m doing. I have also taken the precaution of analyzing the PCAP file in a Windows Sandbox, which just takes a couple of seconds to deploy and run.

The capture file I’m looking at is called “2021-05-13-Hancitor-traffic-with-Ficker-Stealer-and-Cobalt-Strike.pcap” and can be downloaded from here: https://malware-traffic-analysis.net/2021/05/13/index.html

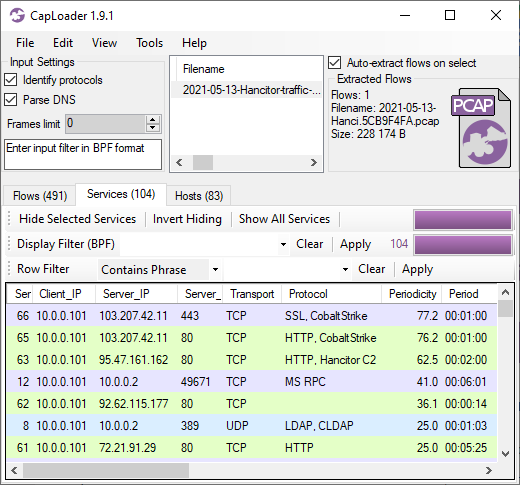
CapLoader’s Services tab shows us that the connections to TCP 80 and 443 on 103.207.42.11 are very periodic, with a detected period of exactly 1 minute. CapLoader successfully identifies the protocols for these two services as Cobalt Strike over HTTP and Cobalt Strike over SSL, respectively. The third service in this list is also very periodic, that’s the Hancitor trojan beaconing to its C2 server every two minutes.

Services tab in CapLoader

CapLoader uses machine learning to identify the application layer protocol based on the behavior of the traffic, not the port number. This means that there can be false positives, i.e. the protocol classification that CapLoader gives a flow or service might be wrong. It is more common, however, for CapLoader to yield false negatives, which means that it can't identify the protocol. The detection of Cobalt Strike inside of HTTP and SSL traffic was recently introduced in the latest 1.9 release of CapLoader. I expected this feature to detect Cobalt Strike traffic in HTTP, but I was delighted to see that CapLoader often detects even TLS encrypted Cobalt Strike beaconing with really good precision!

As shown in the video, the Cobalt Strike beacon config can easily be extracted from the network traffic using NetworkMiner and Didier Stevens’ 1768 K python script.

The output from Didier’s 7868.py tool looks something like this:

0x0001 payload type 0 windows-beacon_http-reverse_http
0x0002 port 80
0x0003 sleeptime 60000
0x0004 maxgetsize 1048576
0x0005 jitter 0
0x0007 publickey 30819f30[...]
0x0008 server,get-uri '103.207.42.11,/ca'
[...]

As you can see, it uses HTTP for transport with a “sleeptime” of 1 minute (60000 ms) and 0% jitter. This means that a new connection will be made to the Cobalt Strike C2 server every minute. The fact that there was no jitter is what gives this service such a high value in CapLoader’s “Periodicity” column.

Network Forensics Training

Are you interested in learning more about how to analyze network traffic from Cobalt Strike and other backdoors, malware and hacker tools? Then take a look at the live online network forensics classes I will be teaching in September and October!

Posted by Erik Hjelmvik on Monday, 31 May 2021 08:30:00 (UTC/GMT)

Tags: #Netresec #Cobalt Strike #CobaltStrike #periodicity #Protocol Identification #PIPI #CapLoader #1768.py #Windows Sandbox #PCAP #NSM #video #videotutorial

Short URL: https://netresec.com/?b=21536fc


CapLoader 1.9 Released

CapLoader 1.9 Logo

A new version of the PCAP filtering tool CapLoader has been released today. The new CapLoader version 1.9 is now even better at identifying protocols and periodic beacons than before. The user interface has also been improved to make it easier to filter and drill down in network traffic to extract interesting, malicious or unusual traffic.

More Protocols Identified

We’ve added port-independent protocol detection for over 20 new protocols since the last release. The newly added protocols include some that are used by malicious tools and backdoors such as hTran, RevengeRAT, Tofsee and Winsecsrv, as well as legitimate protocols like WireGuard (VPN) and RemoteFX (UDP based remote desktop). We’ve also improved our support for ICS traffic analysis by adding protocol identification of SCADA protocols DNP3 and IEC 60870-5-104.

CapLoader also detects what we call “sub-protocols”, which are communication protocols that use other L7 protocols as transport. We have extended the sub-protocol detection in CapLoader 1.9 to include traffic like Anchor_DNS and dnscat traffic, which both run on top of DNS. We have also added detection of Cobalt Strike beacons over HTTP and HTTPS, even though the latter is quite difficult to detect due to the application data being encrypted.

Improved Usability

CapLoader 1.9 comes with several user interface improvements that help you solve the “needle in the haystack” problem even more efficiently than before.

The context menus in the Flows, Services and Hosts tabs can now be used to select rows based on values in any column, such as “Select all flows where Duration > 10 minutes” (when right-clicking a 10 minute flow).

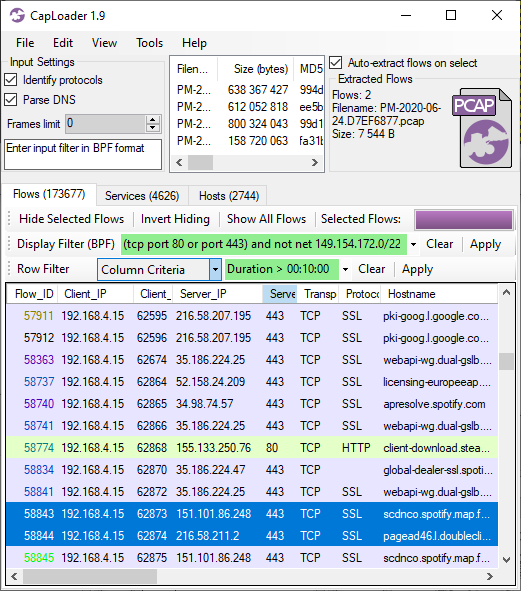
The “Keyword Filter” is now called “Row Filter” in order to avoid getting it mixed up with the “Find Keyword” feature. The Row Filter has also been enhanced with a new filtering mode, to complement the Contains / All Words / Any Words / RegEx options, which is called “Column Criteria”. The Column Criteria can be used to filter the displayed rows based on the values in a user-specified column. The Column Criteria “Duration > 00:10:00” will, for example, only show flows that are 10 minutes or longer, while “ASN = 3301” shows the flows going to Telia’s AS3301.

CapLoader 1.9 with Column Criteria Row Filter Duration > 00:10:00

Image: CapLoader with Row Filter Column Criteria "Duration > 00:10:00"

We have also extended CapLoader's BPF implementation to support VLAN id’s, so that you can use expressions like “vlan 100” as input filter as well as display filter. The BPF implementation also supports logic operators, so that more advanced filters like “(tcp port 80 or port 443) and not net 149.154.172.0/22” can be used.

CapLoader has a method for detecting periodic connection patterns, which was introduced in CapLoader 1.4. This feature can be used to detect clients that connect to a service at regular intervals, such as a beacon used for command-and-control or email client connecting to a mail server. We have improved the periodicity detection in CapLoader 1.9 so that it now detects periodic services more accurately.

The Initial Round Trip Time (iRRT) in the Flows and Services tabs is now measured in milliseconds instead of seconds in order to avoid “bulky numbers” (h/t Eddi).

There was previously a significant delay when selecting many flows at once (like 100.000). We’ve improved the performance of this feature in CapLoader 1.9, so that you can now select several hundred thousands flows at once without having to wait for an unresponsive GUI to update.

More OSINT Lookup Services

A feature in CapLoader that often comes in handy is the ability to right-click a flow, service or host and open a website with OSINT information about the clicked IP address or domain name. We have now replaced some of the OSINT services with new better ones.

The new services we’ve added to CapLoader 1.9 for performing online OSINT lookups of IP addresses, network services and domain names are:

Bug fixes and Credits

Several bugs have been fixed in this new release of CapLoader, much thanks to feedback we’ve received from our users. We’d like to thank Anders Regert and Mandy van Oosterhout for reporting bugs in CapLoaders “Save As” feature. We’d also like to thank Hyun Dowon for reporting a snap length corruption bug that previously appeared when exporting flows from Pcap-NG files We have also fixed an issue where capture files were previously not always merged in chronological order when being aggregated.

Updating to the Latest Release

Users who have purchased a license for CapLoader can download a free update to version 1.9 from our customer portal. All others can download a free 30 day trial from the CapLoader product page (no registration required).

Posted by Erik Hjelmvik on Tuesday, 25 May 2021 12:20:00 (UTC/GMT)

Tags: #Netresec #CapLoader #PCAP #Pcap-NG #IEC-104 #CobaltStrike #BPF #periodicity #OSINT

Short URL: https://netresec.com/?b=2159bda


Running NetworkMiner in Windows Sandbox

NetworkMiner can be run in a highly efficient Windows Sandbox in order to analyze malicious PCAP files in Windows without accidentally infecting your Windows PC. This blog post shows how to set up a Windows Sandbox that always boots up a fresh install of Windows 10 with the latest version of NetworkMiner installed.

I generally recommend analyzing Windows malware in Linux, or some other non-Windows environment, in order to avoid accidentally infecting yourself (NetworkMiner runs fine in Linux btw). Nevertheless, I still often find myself loading capture files containing malicious network traffic into CapLoader and NetworkMiner under Windows. I have previously demonstrated that this can be a quick and crude way to perform an anti virus scan of files contained in a pcap file.

Windows Sandbox

If you want to analyze malicious traffic in Windows with minimal risk of infecting yourself then you should definitely check out Microsoft’s Windows Sandbox (available in Windows 10 Pro and Enterprise editions). The Windows Sandbox is using Windows containers, so it’s very efficient compared to spinning up a full Windows VM. It also provides features like kernel isolation, so that the sandbox container doesn’t use the same kernel as the host, and ensures that a new Windows environment is created every time the sandbox is run. Windows Sandbox also doesn't run any anti-virus, so it won't interfere with the extraction of malicious contents from within the analyzed capture files.

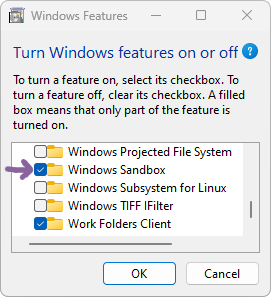
Optional Features, Windows Sandbox Follow these steps to install Windows Sandbox:
  1. Run OptionalFeatures.exe, aka “Turn Windows features on or off”
  2. Enable the “Windows Sandbox” feature (check the box)
  3. Reboot

Or run this PowerShell command as administrator and then reboot:

Enable-WindowsOptionalFeature -FeatureName "Containers-DisposableClientVM" -All -Online

Then create a sandbox config, which downloads and installs the latest version of NetworkMiner every time the sandbox is started, by creating a file called “NetworkMinerSandbox.wsb” with the following contents:

<Configuration>
  <MappedFolders>
    <MappedFolder>
      <!-- Replace path below with your PCAP dir -->
      <HostFolder>C:\Users\Erik\pcap</HostFolder>
      <ReadOnly>true</ReadOnly>
    </MappedFolder>
  </MappedFolders>
  <LogonCommand>
    <Command>cmd.exe /C "curl -L https://www.netresec.com/?download=NetworkMiner | tar -C C:\Users\WDAGUtilityAccount\Desktop\ -xf -"</Command>
  </LogonCommand>
</Configuration>

Note: Replace “C:\Users\Erik\pcap” with whatever location your capture files are at

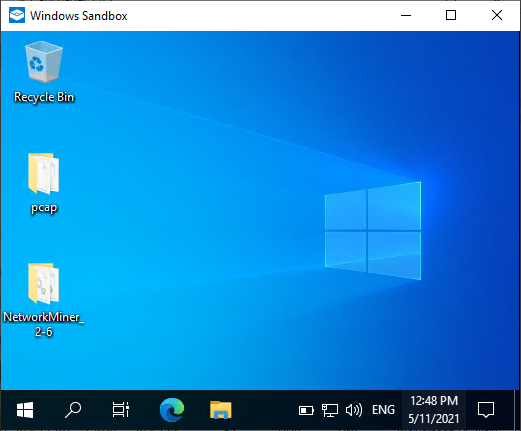
After starting NetworkMinerSandbox.wsb you’ll have a fresh Windows machine up and running within a couple of seconds. The latest version of NetworkMiner and your PCAP dir are both accessible from the sandbox’s desktop.

Windows Sandbox

Image: NetworkMiner 2.6 installed in a clean Windows Sandbox environment

Moving files in or out of the sandbox is just a matter of copy and paste (Ctrl+C / Ctrl+V).

VirtualBox and Windows Sandbox

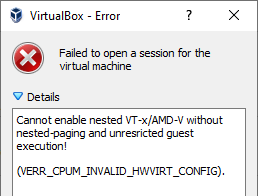
VirtualBox error message Cannot enable nested VT-x/AMD-V without nested-paging and unrestricted guest execution

Are you using VirtualBox to run virtual machines on your Windows host and getting an error message saying “Failed to open a session for the virtual machine”, with details such as “Failed to get device handle and/or partition ID” (VERR_NEM_VM_CREATE_FAILED) or “Cannot enable nested VT-x/AMD-V without nested-paging and unrestricted guest execution”, after enabling Windows Sandbox?

Even though Windows Sandbox doesn’t need Hyper-V it still requires a hypervisor, which unfortunately conflicts with VirtualBox. You can disable the hypervisor by running the following command as administrator:

bcdedit.exe /set hypervisorlaunchtype off

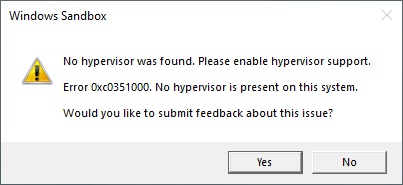
...and then restart the computer. Turning off the hypervisor will unfortunately prevent Windows Sandbox from running, giving an error message saying “No hypervisor was found. Please enable hypervisor support.” (Error 0xc0351000)

Windows Sandbox error message No hypervisor was found. Please enable hypervisor support. Error 0xc0351000. No hypervisor is present on this system

To re-enable the hypervisor, in order to run Windows Sandbox again, you’ll need to run

bcdedit.exe /set hypervisorlaunchtype auto

and restart the host.

Update May 26, 2021

We have now uploaded a simple Windows Sandbox config to our website here:

https://www.netresec.com/?download=NetworkMinerSandbox

This script runs on any Windows Pro machine that has the Sandbox feature active.

Posted by Erik Hjelmvik on Tuesday, 11 May 2021 13:39:00 (UTC/GMT)

Tags: #Netresec #NetworkMiner #PCAP #Windows #Sandbox #Windows Sandbox #Malware

Short URL: https://netresec.com/?b=215d5b5

2021 March

Live Online Training - PCAP in the Morning

2021 January

Finding Targeted SUNBURST Victims with pDNS

2020 November

PolarProxy 0.8.16 Released

2020 January

RawCap Redux

2018 November

Remote Packet Dumps from PacketCache

2018 August

NetworkMiner 2.3.2 Released!

2018 April

NetworkMiner 2.3 Released!

2018 February

Examining Malware Redirects with NetworkMiner Professional

Analyzing Kelihos SPAM in CapLoader and NetworkMiner

Antivirus Scanning of a PCAP File

Zyklon Malware Network Forensics Video Tutorial

2017 April

Network Forensics Training in London

2017 February

10 Years of NetworkMiner

2017 January

Network Forensics Training at TROOPERS 2017

2016 October

Reading cached packets with Wireshark

Detect TCP content injection attacks with findject

2016 September

Bug Bounty PCAP T-shirts